
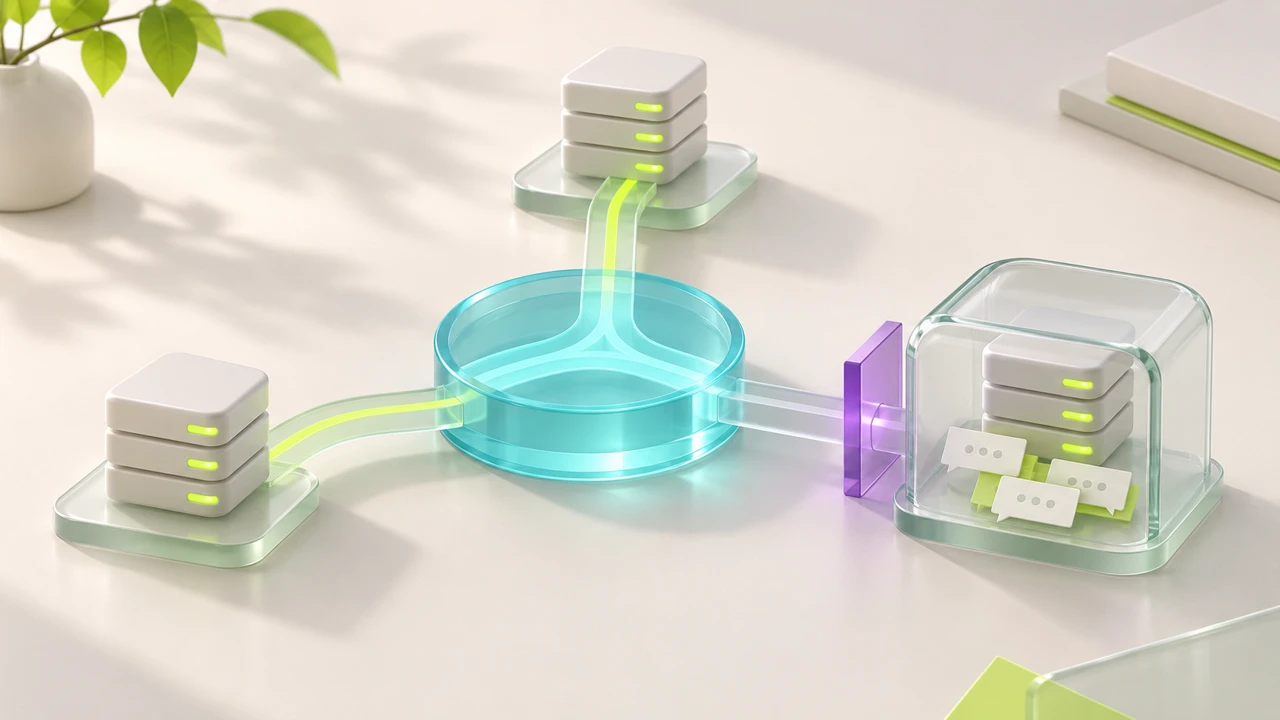
A retention label needs an accountable route
OpenRouter says potentially affected customers were notified and further verification is underway. Our reading is that eligibility removal should be understood as a change in trust status, rather than proof that every removed endpoint suffered the same breach.
For a development team, a useful inventory would connect the application, API key, router, selected endpoint and retention setting. Without that mapping, changing a policy in one dashboard can leave uncertainty about requests made earlier or through another route. This is an operational implication of the disclosures, not a claim that we audited customers’ configurations.
What the researchers actually measured
Dragos reported on November 19 that it submitted roughly two million prompts with trackable canaries over July–November. It described provider compromises, reseller access and apparent privacy-policy failures. The researchers caution that a triggered canary does not by itself locate the leaking hop.
That limitation separates detection from attribution. Evidence that someone later accessed a planted URL can establish exposure, while identifying the responsible service requires additional routing and incident evidence. The test population also should not be read as a count of real customers or a measurement of every AI provider.
Together’s disclosure concerns retained samples
Together AI’s November 21 notice says a credential committed by an AI coding agent exposed a private repository containing June and July prompt samples. An unauthorized party downloaded them. The company says review of affected contents continues and new accounts now default to ZDR.
The sample dates and disclosure date answer different questions: one identifies the historical requests involved, the other when customers received the public explanation. Our interpretation is that removing retention can reduce the material available for theft, while credential controls address a separate access mechanism. Neither control should be treated as a substitute for the other.
What remains unresolved for users
The public material does not provide one complete customer-impact total across all providers. We therefore cannot translate endpoint removals into a number of leaked conversations, and we do not infer that every request routed through OpenRouter was compromised.
Our practical conclusion is to reconcile provider notices with the routes an application actually used before estimating exposure. A secret embedded in a prompt and ordinary confidential text call for different response decisions. This article reports the coordinated disclosure and response together; it does not present the older sample collection as a fresh November data capture.
Discussion.
Your perspective matters. Sign in, pick a nickname and choose your cyber identity.
Loading discussion…
Your account name, email and photo stay off your comments.