What the report describes
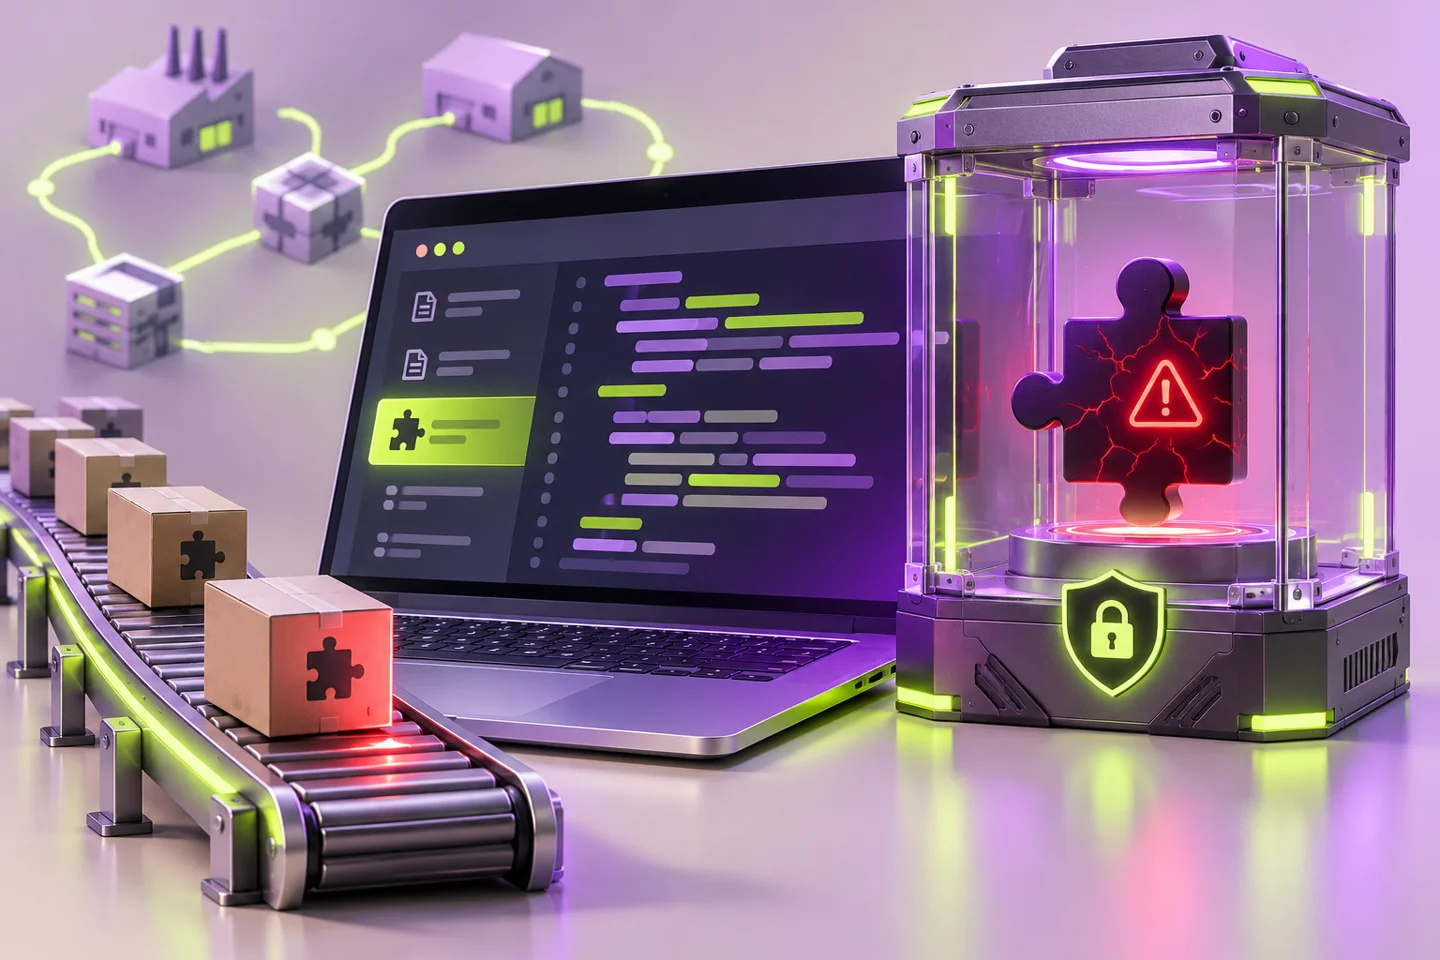
Cursor says the attacker accessed historical agent traces, some containing unredacted credentials, and then reached selected internal services. A stolen credential was subsequently used to place unauthorized Anthropic.claude-code builds in Cursor’s own marketplace cache. The company explicitly distinguishes that cache from Open VSX and says Anthropic did not publish the malicious copies. That distinction matters: an extension’s name alone does not identify which organization or distribution stage was compromised. The incident concerns a specific supply-chain path, rather than evidence that every copy of the named extension was malicious.
Which installations need checking
Cursor identifies versions 2.1.312 and 2.1.313 and an exposure window on October 29. Potentially affected customers are directed to the official security notice, which warns that uninstalling the extension alone may be insufficient. We are not substituting a generic cleanup script for those system-specific instructions. Administrators should check installed versions, installation times, organization notifications and the current vendor notice. Remediation code from random comments or unsolicited messages should not be treated as authoritative merely because it mentions the same incident.
Attribute the scope carefully
Cursor states that most customers were unaffected and that it believes the incident is contained. These remain attributed vendor statements, not an independent forensic conclusion by our publication. The account separates historical analysis data from current production systems and identifies different categories of potential exposure. That is more informative than treating the word breach as a uniform risk for every customer. This article records the November 13 update; subsequent material findings should update the same event instead of producing multiple near-identical stories from different news outlets.
The engineering implication
Our assessment is that agent traces can become a secret-bearing data store, and extension caches belong inside software supply-chain controls. A security review therefore needs to consider trace retention, supplier keys, internal service permissions and package-distribution integrity. The lesson is specific rather than a reason to reject every AI editor: evaluate access boundaries and incident-notification procedures alongside model features. For affected organizations, the immediate evidence remains their own installation history and the official remediation guidance, not an assumption drawn from a product name or a generalized headline.